Loading posts ...

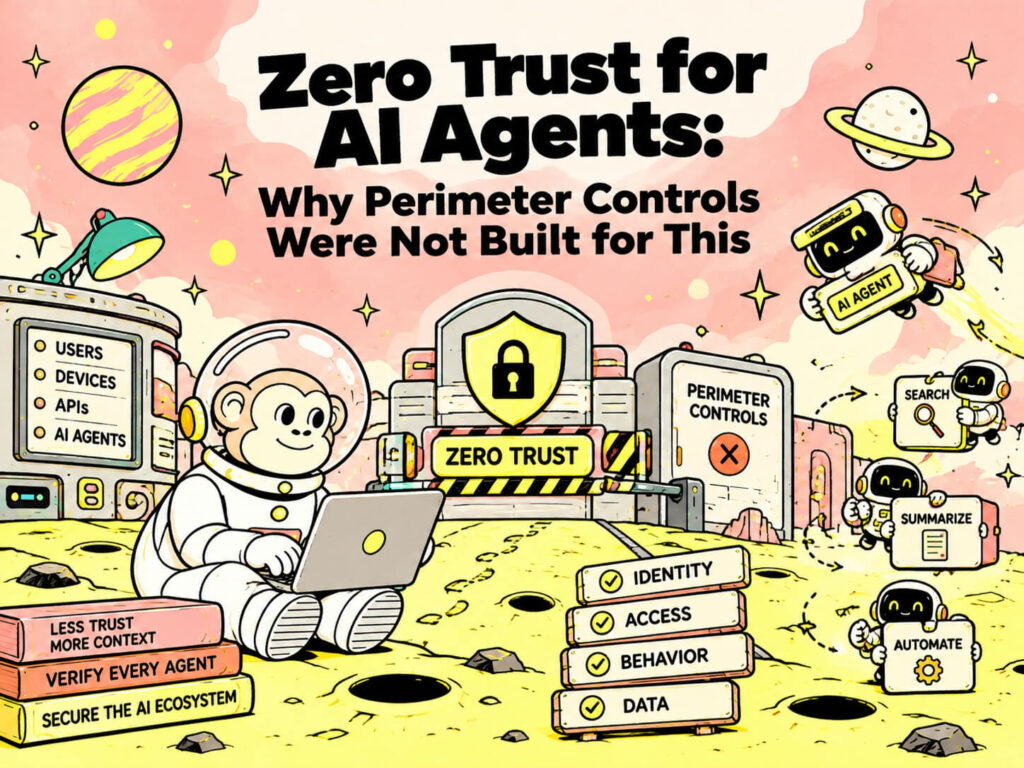
Zero Trust for AI Agents: Why Perimeter Controls Were Not Built for This

AI agents are reshaping enterprise computing’s security model. Traditional applications execute predefined logic. Human users make decisions, and applications enforce them. AI agents introduce a third category: non-human software principals that can interpret context, make…
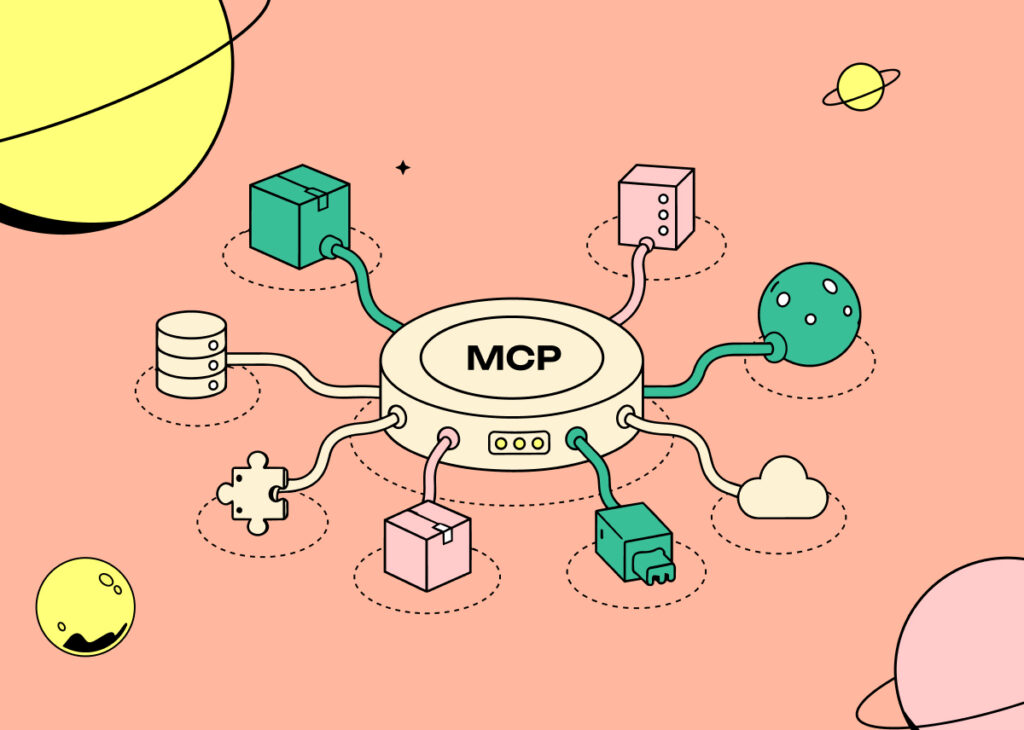
Top MCP Security Risks Enterprises Need to Address

At the center of the rapid evolution of agentic AI is the Model Context Protocol (MCP). MCP is an emerging open standard that enables AI…
Read More

Load/Mine: A Hugging Face Malware Campaign Returns After Takedown

Pluto Research tracked a cryptomining and backdoor campaign across Hugging Face model repositories. The investigation follows related accounts, analyzes the payload, and documents the campaign’s…
Read More

How Prompt Injection Attacks Work and Why AI Agents Make Them Dangerous

AI security is moving beyond whether a model can generate unsafe content. The more consequential question is whether an attacker can manipulate an AI system…

ChatGPT Dots Security: A Practical Hardening Guide

A practical security hardening guide to ChatGPT dots. Learn which controls apply to cloud and local access, where Custom rules fall short of enforcement, and…
Read More

Inside Personal AI Assistants: What to Check in Grok Bot, ChatGPT dots, and Meta Muse

Personal AI assistants keep working without continuous supervision, remember what they are told, and run on a computer your team never provisioned. Pluto Research maps…
Read More

Welcome to Planet Pluto!

Pluto Security is out of stealth with $42M funding! Exactly one year ago, Pluto was an idea. A very strong idea, with a very clear…
Read More