

A compromised laptop rarely looks compromised: the user remains signed in, and every request carries valid credentials. That is why Zero Trust no longer treats a login as proof of anything. An AI agent sits in the same spot, holding real access that untrusted text can steer, and Zero Trust AI handles it the same way.
Zero Trust AI Starts by Assuming the Agent Is Compromised
NIST SP 800-207 describes zero trust as assuming there is “no implicit trust granted to assets or user accounts based solely on their physical or network location.” Other zero trust principles build on that, plus one more habit: plan as if the breach has already happened.
For a laptop, the breach might involve a phishing payload or a malicious browser extension. For an agent, it is usually easier, because no password needs to be stolen. An attacker only needs to plant instructions somewhere the agent will read them, such as a support ticket, a README in a cloned repo, or a tool response, and the agent then uses its own valid permissions on the attacker’s behalf.
So the design question changes. You stop asking whether you can trust the agent and start asking how much damage it can do once it can’t.
An AI Agent’s Access Compared With a Compromised Laptop’s
The overlap is closer than most teams expect. A coding agent on a developer workstation inherits the developer’s SSO sessions, cached cloud credentials, and API keys stored in local config files. To the endpoint, the agent is the user. Pluto’s write-up on AI agent authorization shows how that inherited context lets an agent’s real reach drift well past its task.
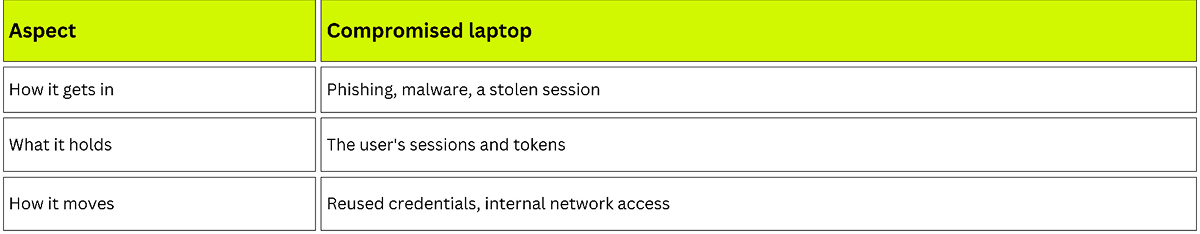
The key differences are speed and breadth. An agent can chain many tool calls in the time it takes a person to make one, and it rarely starts with least-privilege access. Many simply run with whatever the human had, because scoping an agent down takes deliberate work.
Why Zero Trust Verifies Every Agent Action, Not Just the Login
A single identity check at login made more sense when a session meant a person clicking through one app. An agent session can involve hundreds of decisions, each shaped by whatever the agent read last.
Continuous verification moves the check to the action. Each tool call is evaluated against the task it belongs to: who the agent is acting for, what it is touching, and whether the request fits the job. Picture an agent asked to summarize one support ticket that then calls the CRM’s bulk export endpoint. The token is valid, and the session is fine, yet the action is far outside its scope. A login check lets that through, while a per-action policy check blocks it.
Short-lived, task-scoped credentials back this up. A token that expires in minutes gives an attacker much less to work with than a long-lived key copied into an .env file.
Containing an Agent the Way Zero Trust Isolates an Infected Device
When an endpoint tool flags a laptop, responders isolate it. The device loses network access, its sessions are revoked, and its state is preserved for investigation. Microsegmentation does the quieter work beforehand, so a compromised host can reach only a small slice of the environment.
Agents need both layers, and both depend on the agent having its own identity. If it borrows a developer’s token, you cannot cut one off without locking out the other.
- Dedicated identity: Revoke the agent without touching the human’s access.
- Scoped tools: Expose only the tools and MCP servers the task needs.
- Egress allowlists: Limit outbound calls to approved destinations.
- Action-level logs: Record prompts, tool calls, and results for the investigation.
None of it works without an inventory, which Pluto’s guide to enterprise AI security at scale calls the usual first step. You cannot isolate an agent nobody knew was running.
Final Thoughts
Treating an agent like a compromised laptop does not mean agents are malicious. It is a statement about where trust comes from. A laptop is not trusted because it sits on the corporate network, and an agent should not be trusted because it holds a valid token. Apply continuous verification to every action, keep access narrow, and ensure you can shut the agent off on its own. Zero Trust AI is mostly the endpoint playbook security teams already run, applied to a new kind of endpoint.