Pluto is officially out of stealth, with $42 million in total funding. Read here

About the author

Yotam Perkal leads Security Research at Pluto Security, where he focuses on securing AI-native development environments and uncovering emerging risks in AI-driven software workflows. With over a decade of experience in cybersecurity, his work sits at the intersection of offensive research, vulnerability management, and software supply chain security.

Previously, Yotam led Threat Research at Zscaler, headed Vulnerability Research at Rezilion, and held multiple roles within the PayPal security organization.

He is an active contributor to cross-industry initiatives focused on AI security, vulnerability management, and software supply chain risk.

Related Posts

Securing Claude Tag: A Practical Hardening Guide

Claude Tag’s security comes almost entirely from configuration – who can invoke it, what each channel and connected repo can reach, where its data can…

The Importer Syndrome × Count Dooku 2.0 – When Your New AI IDE Imports More Than Extensions

How a gap between Microsoft Marketplace and Open VSX lets attackers hand you malware under trusted names, and the 150-extension campaign already exploiting it. TL;DR…

Inside Claude Tag: How Anthropic’s Slack-Native Agent Actually Works

Claude Tag drops an autonomous, credentialed AI agent into your Slack – one that acts under its own identity, can be summoned by anyone in…

Total Recall: How Two CVEs Let Any Website Read, Rewrite, and Wipe Your AI’s Memory

CVE-2026-33010 (CVSS 8.1) and CVE-2026-29787 (CVSS 5.3) in mcp-memory-service – a popular “second brain” for AI assistants – let a single malicious link silently steal,…

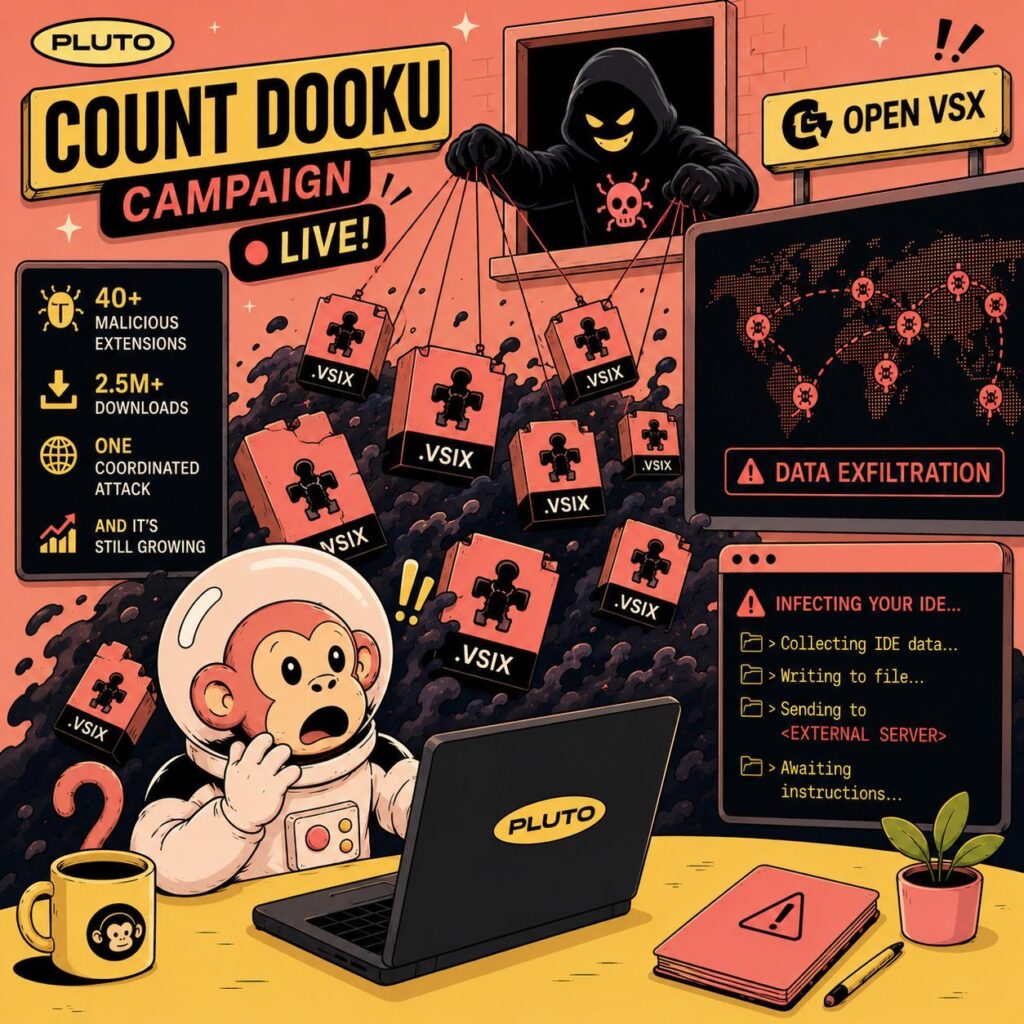
Count Dooku: A Live Malicious Open VSX Campaign Hiding in Plain Sight

Last updated: June 30, 2026 The most dangerous supply chain attacks are not always the loud ones. Over the last few days, Pluto Security has…

Introducing Plutonium

Over the past months we launched ClaudeSec for the Anthropic ecosystem and copilotsec.ai for the Microsoft one. Each closed the same gap in its own…

Unauthenticated Remote Code Execution in HuggingFace Transformers via Config Injection

One Line. Zero Warnings. Full Compromise. What we found: A critical RCE vulnerability in HuggingFace transformers: CVE-2026-4372 – Config injection via _attn_implementation_internal triggers unsandboxed remote…

Introducing CopilotSec: A Community Knowledge Hub for Security of The Microsoft AI Ecosystem

The Microsoft AI ecosystem has expanded faster than the practical security guidance around it. Copilot Studio gives any citizen developer a citizen-grade path from idea…

Securing Copilot Studio: A Practical Hardening Guide

Copilot Studio has gone from “we’re experimenting” to “we have agents in production” in a lot of organizations – and the security work hasn’t kept…